Your security never sleeps. Neither does our AI.
A 24/7 AI-powered Security Operations Center that detects, triages and responds in minutes, combining machine-speed analysis with seasoned human analysts.
soc · how triage works
Escalated to an analyst
Critical
Impossible-travel sign-in · finance-svc
AI · escalated
Brute-force blocked · edge-gw-02
auto-closed
New device enrolled · MFA verified
benign
Suspicious PowerShell · host-4471
analyst
Powered by
Microsoft Sentinel Defender XDR NIST CSF 2.0 MITRE ATT&CK GreyCortex
AI triage
Machine speed on the noise
Analyst validated
A person confirms each escalation
24/7/365
Continuous monitoring & response
Sentinel-native
Cloud, identity, endpoint and network
One platform, four lenses
However you need to see your security, we have the view.
Where AI does the heavy lifting
Machine speed on the noise. Human judgment on what matters.
Noise reduction
AI clusters and dedupes alerts, suppressing the benign so analysts never chase ghosts.
benign alerts suppressed
Signal correlation
Cross-source correlation links weak signals into a single high-confidence incident.
cloud · network · identity
Guided response
Recommended containment and automated playbooks cut response from hours to minutes.
minutes, not hours
Inside the platform
Real dashboards. Real-time posture.
Pre-aggregated metrics from Microsoft Sentinel, rendered for the people who need to act on them.
Posture overview
Effectiveness
Controls register
Control detail
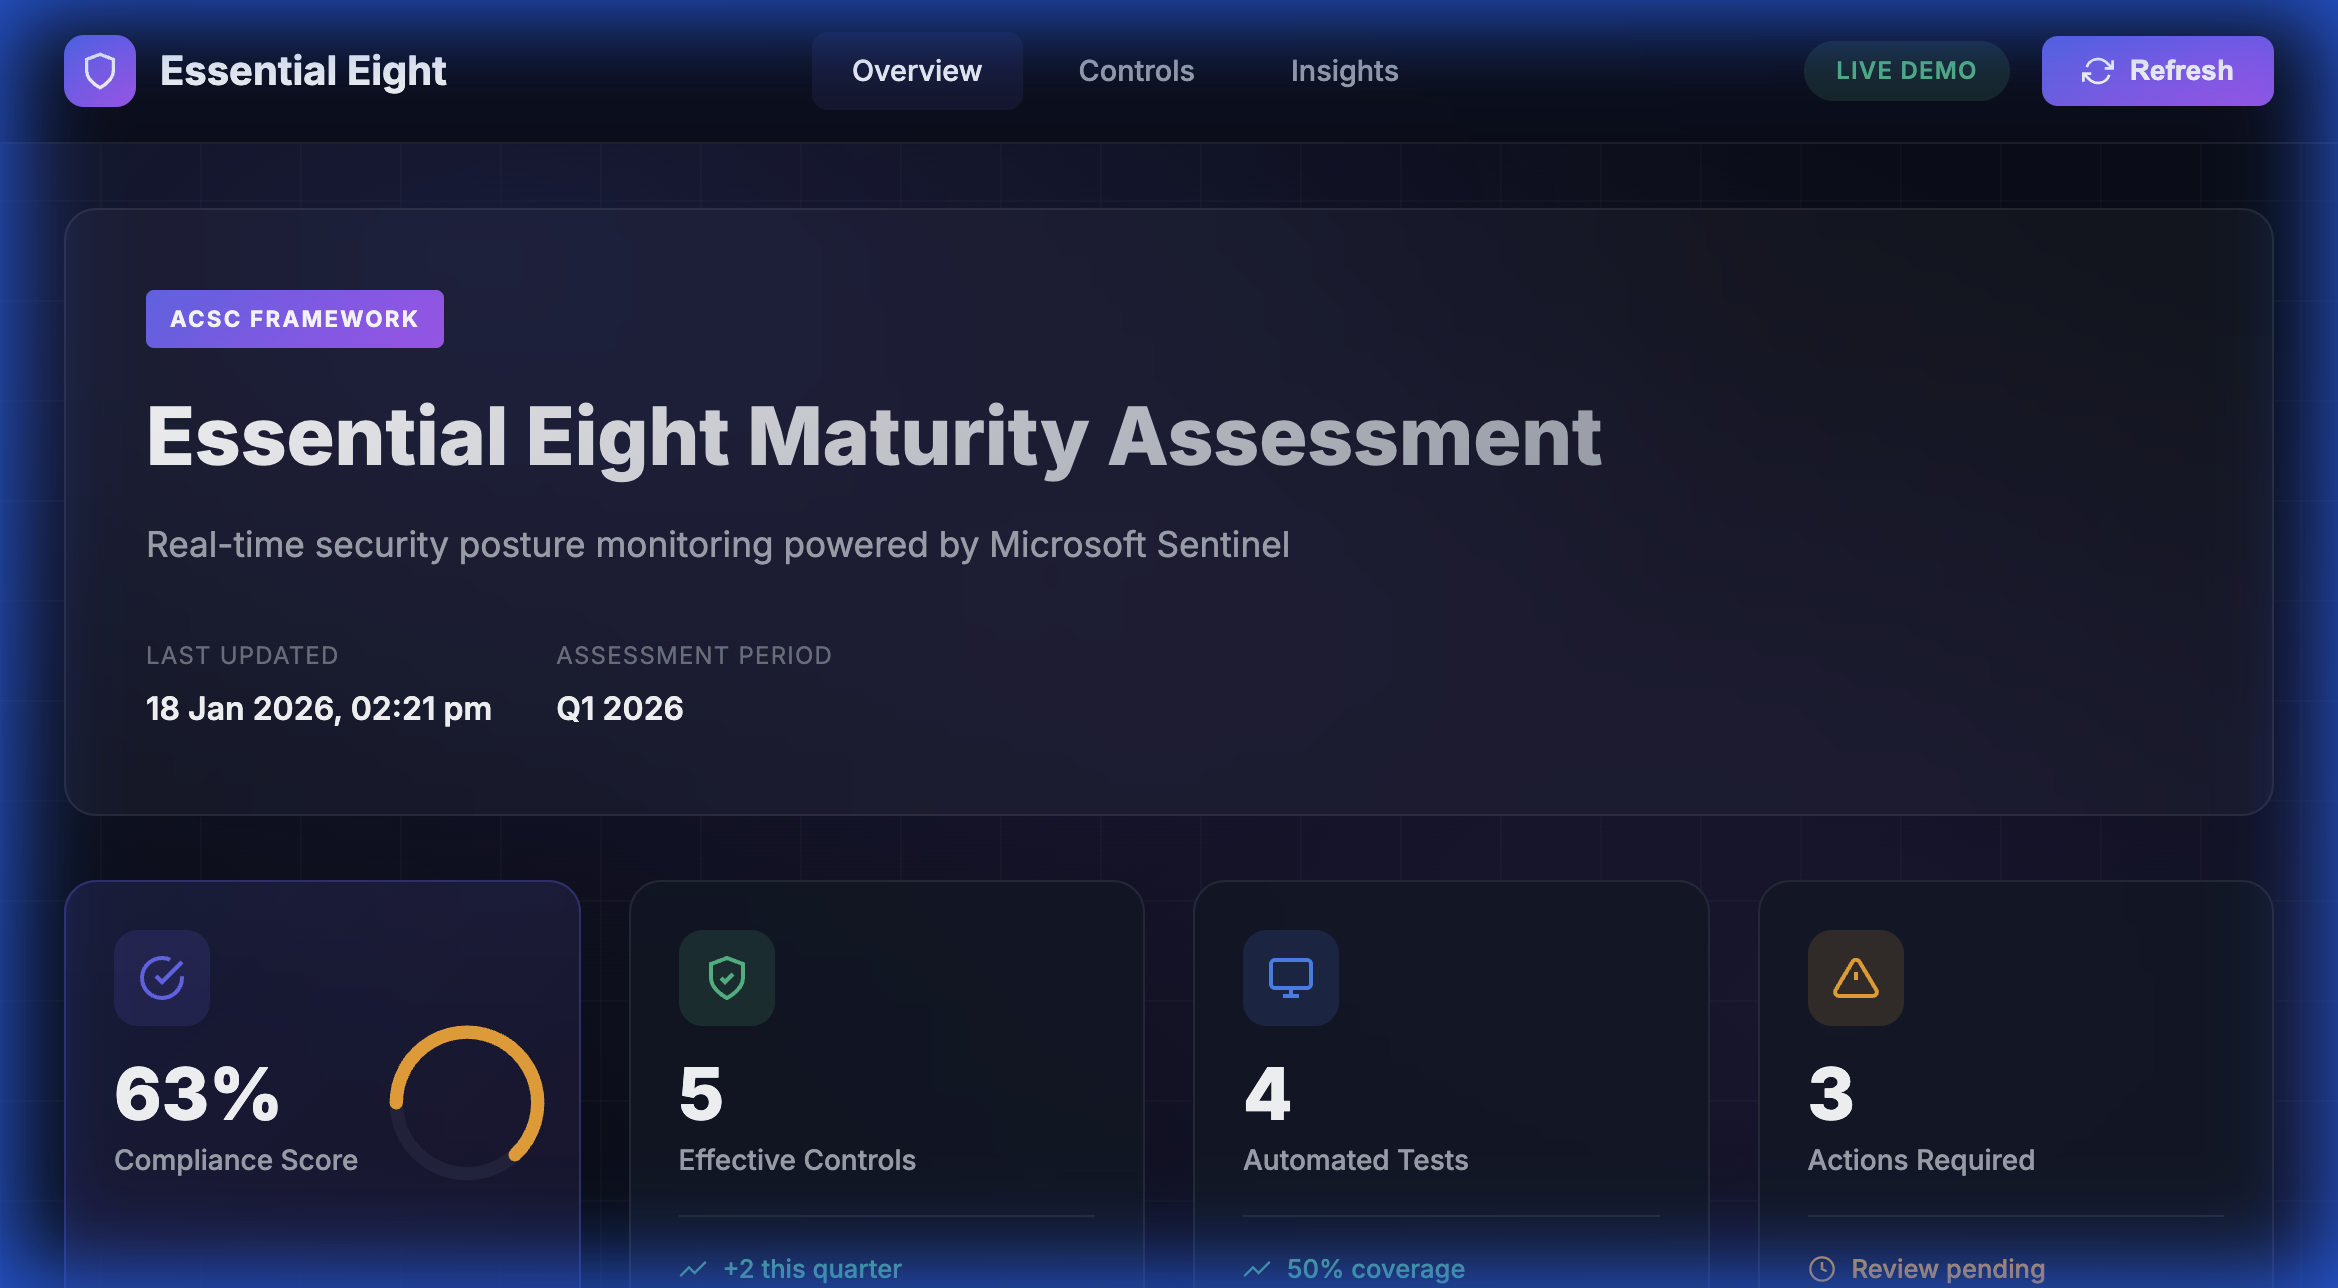
Compliance posture overview: framework maturity scoring, powered by Microsoft Sentinel.
Built for every role
A view tuned to the question you're asking.
ANALYST
SOC Analyst
"What do I work on right now?"
Open incidents, new alerts, aging buckets, top affected entities.
LEAD
SOC Lead
"Is the SOC keeping up?"
MTTA & MTTR (median + P95), inflow trends, closure rate, top rules.
TELEMETRY
Telemetry Health
"Is Sentinel healthy?"
Ingestion by table, detection coverage, zero-ingestion alerts.
CUSTOMER
Customer View
"How are we protected?"
Customer-scoped incidents by severity, status and trend.
From signal to resolution
How the SOC works
01
Ingest
Sentinel collects telemetry across cloud, identity, endpoint and network.
02
AI triage
Models score, correlate and suppress noise, surfacing real incidents.
03
Analyst validation
Our 24/7 analysts confirm, investigate and decide on response.
04
Respond & report
Contain, remediate and report back with full context and evidence.